
AI Token Fraud Exposed: A Three-Layer Threat
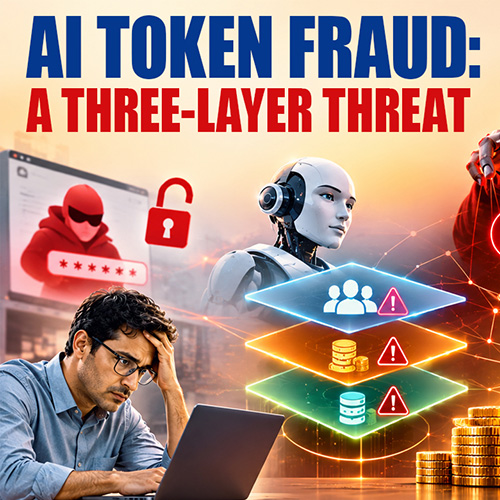
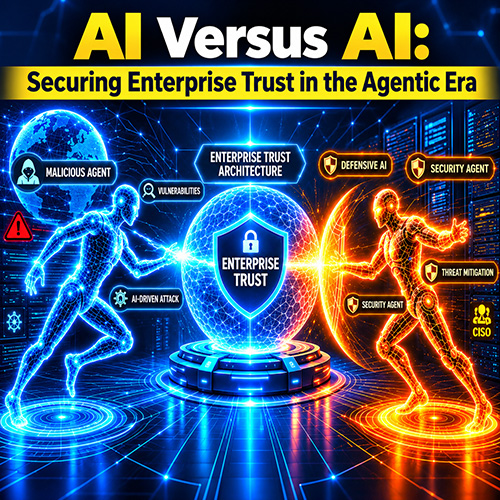
AI token fraud is emerging as a security concern as organisations increasingly rely on AI agents, APIs and automated workflows. The threat can be understood across three layers - Identity and Access Abuse, Token Consumption and Financial Fraud and Data and Workflow Manipulation
AI token fraud is growing across three connected layers.
All of them exploit one weakness: valuable AI credentials are often guarded like ordinary configuration settings.
At the customer level, fake sign-ups are driving the surge.
Stripe links roughly one in six new AI-sector sign-ups to token theft, and some firms report fraud attempts up more than 600%.
Leaked keys make it worse.
A stolen key costing about $30 can generate over $46,000 in charges a day on the victim’s account.
System integrators concentrate the risk.
One compromised gateway, as in the LiteLLM supply-chain breach, can expose every connected client at once.
Opaque billing deepens the problem.
When integrators resell AI usage, clients struggle to tell theft apart from genuine consumption.
The newest threat is autonomous.
Criminal tools like MONST3R-AI now run hacking scans powered by stolen OpenAI, Anthropic and Google keys.
Defenses include secret scanning, key rotation, spending caps, per-client budgets and authenticated model servers.
Without them, stolen compute will keep fuelling more theft.

See What’s Next in Tech With the Fast Forward Newsletter
Tweets From @varindiamag
Nothing to see here - yet
When they Tweet, their Tweets will show up here.